
Privileged remote access,built for the AI era
One self-hosted workspace where your team — and your AI agents — reach every server, network device, cluster, cloud and database. Governed by policy. Recordable for replay.
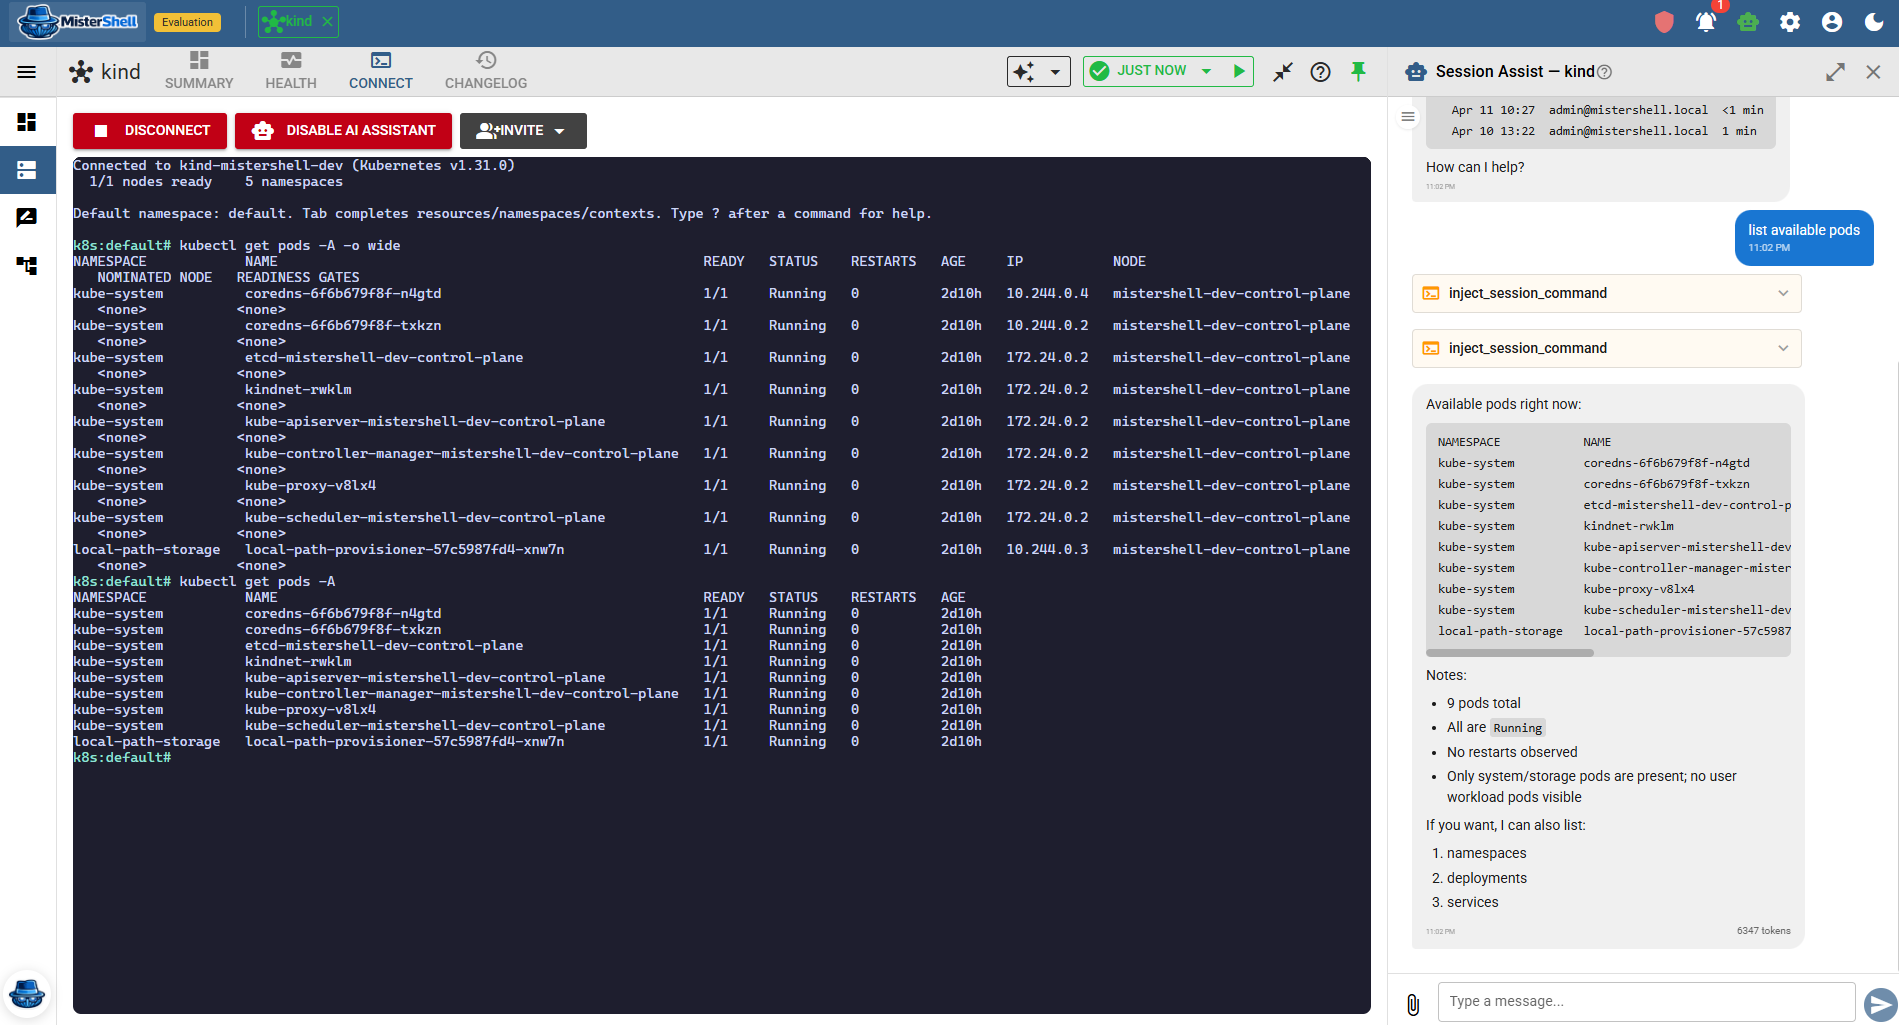
One platform
Access. Governance. AI.
Three jobs, one self-hosted platform — no second tool, no migration.
Access
Every session type — SSH, RDP, VNC, kubectl, database, cloud CLI, and web apps — in the browser or from the SSH client your engineers already use, delivered through outbound-only workers that fit your network segmentation. No VPN sprawl, no per-target tooling.
Privileged remote access →Governance
One set of rules over every way in: session policy with per-command ACLs, approval before access where you require it, recording and replay by policy, and audit events straight to your SIEM. Security sets a rule once — every team, vendor, and agent inherits it.
Unified governance →AI
An assistant that already knows the box — live context, operational facts, history — and AI agents under guardrails: read-only by default, attributed, audited. Bring your own LLM.
AI-assisted operations →Why one platform
One platform instead of many
Every resource — servers, network devices, Kubernetes clusters, databases, cloud accounts — reached the same way by your engineers and by AI: the agents you build here, and the AI tools you already run. One path in, one policy, one record of what happened. Without MisterShell, that takes an access broker, a bastion tier, a recording layer, a SIEM integration for each — and an agent framework you build yourself. A stack that grows another product every time you add a kind of resource, user or AI agent.
Safer
One way in instead of many, with no credentials left sitting on laptops. Every action attributed and replayable — your agents on that same path, not through a side door cut for automation.
Cheaper
No separate access broker, bastion tier, recording layer, team password manager or per-seat terminal client to license and operate — and no agent framework to build and maintain alongside them.
Simpler
One platform to run and upgrade. One policy instead of per-resource configuration. One integration to your SIEM instead of one per tool.
Better security, for less money and less complexity.
See It in Action
A single workspace for monitoring, operations, change tracking and automation.
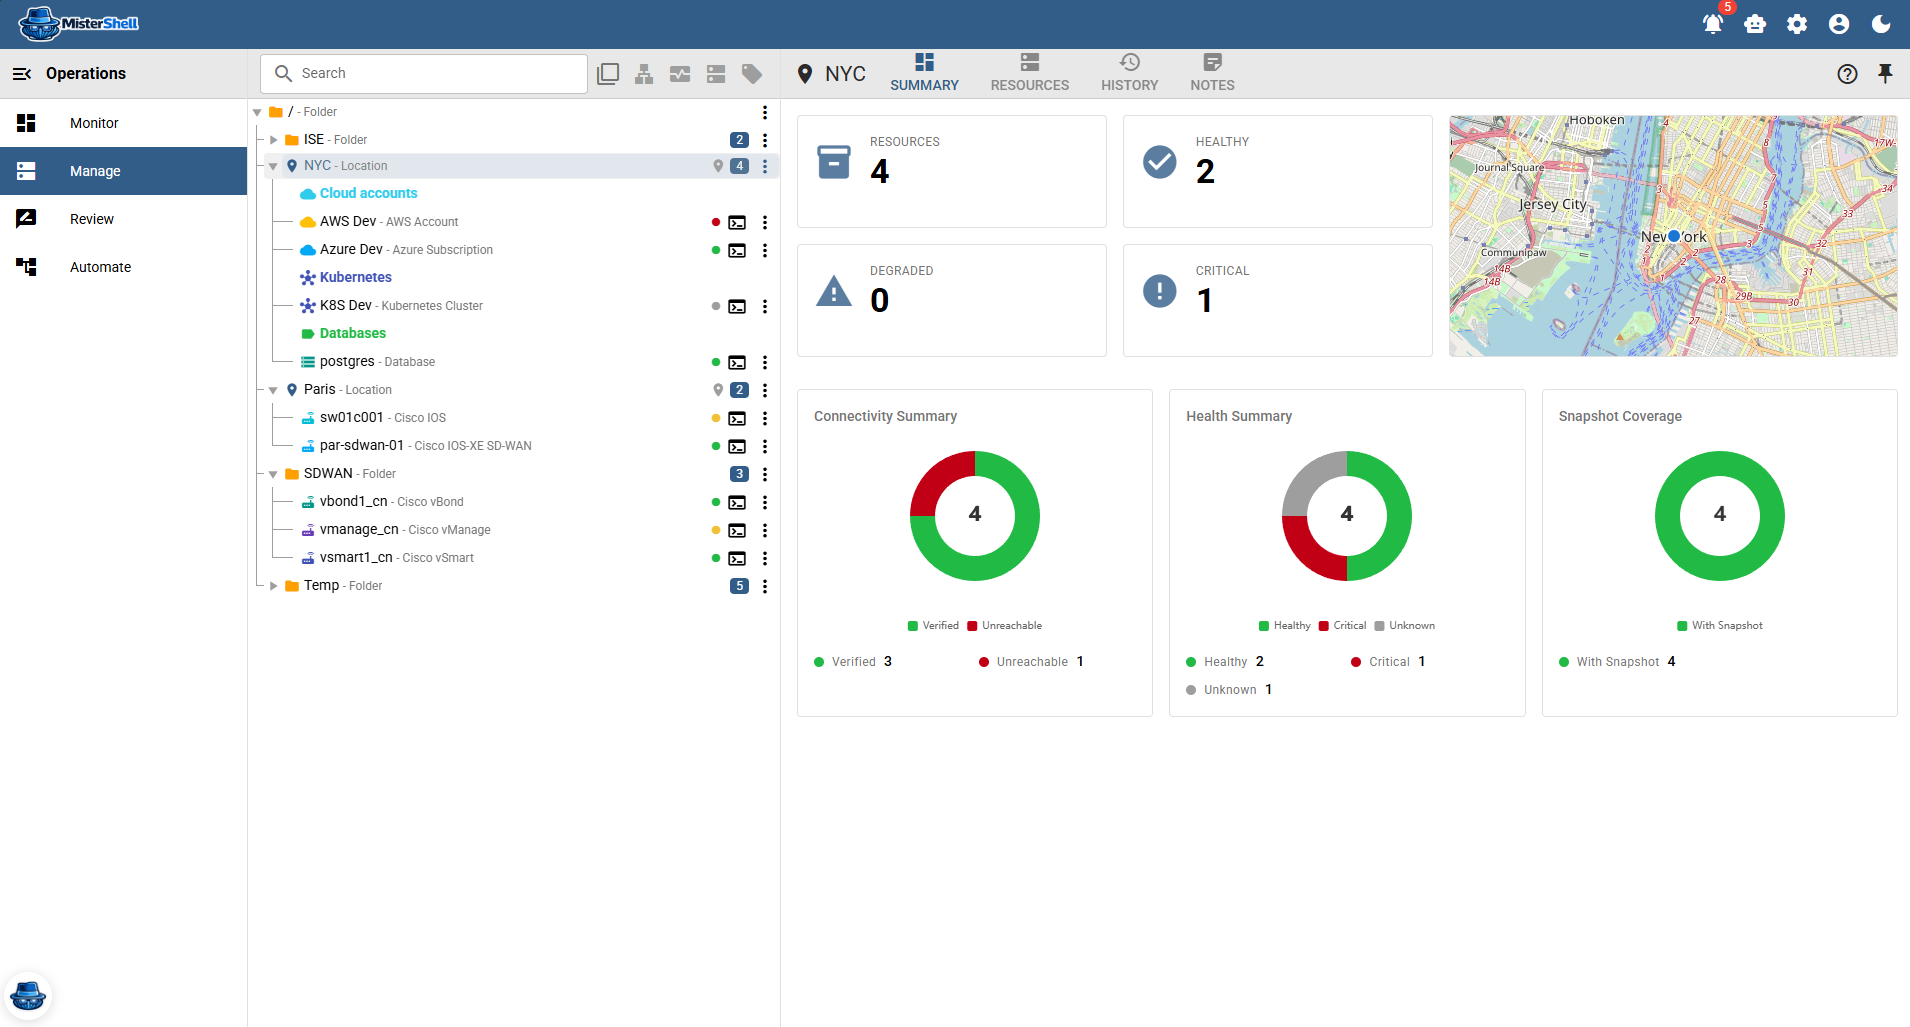
The estate at a glance — locations, inventory, and per-location health and connectivity
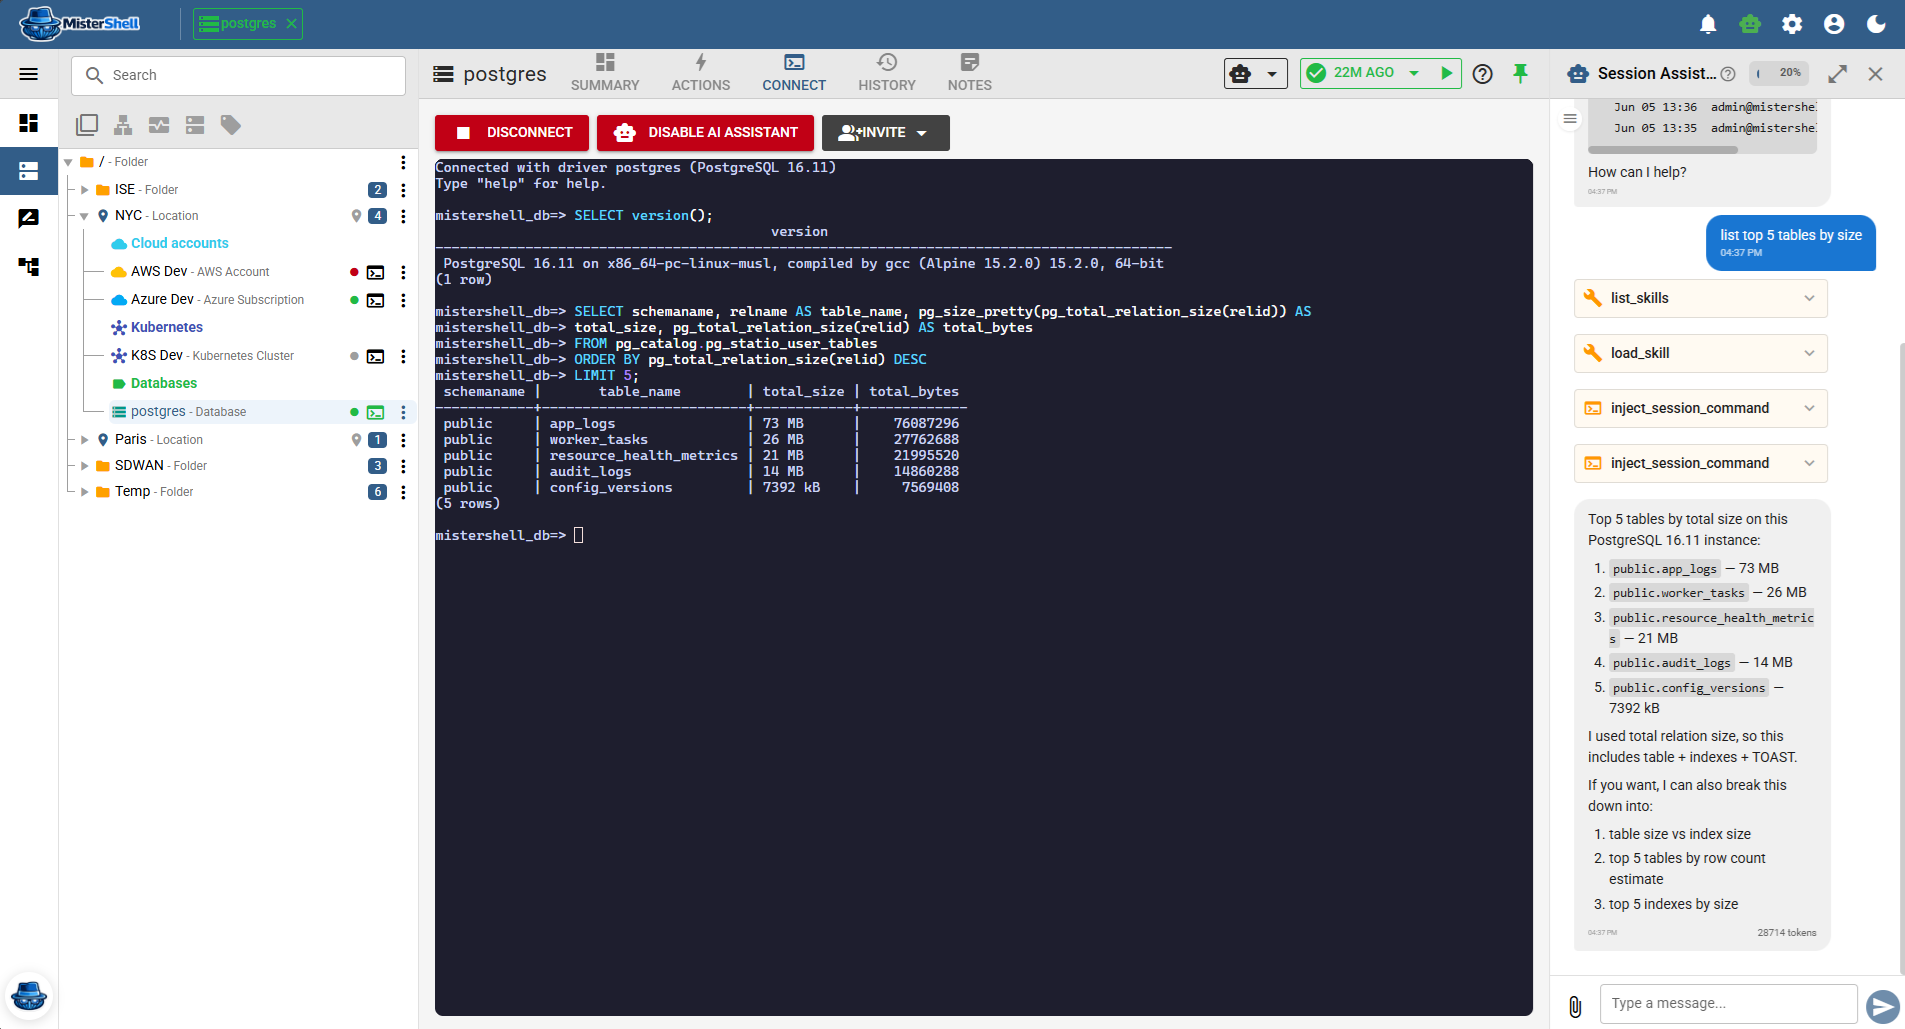
Database sessions in the browser, with AI assistance alongside
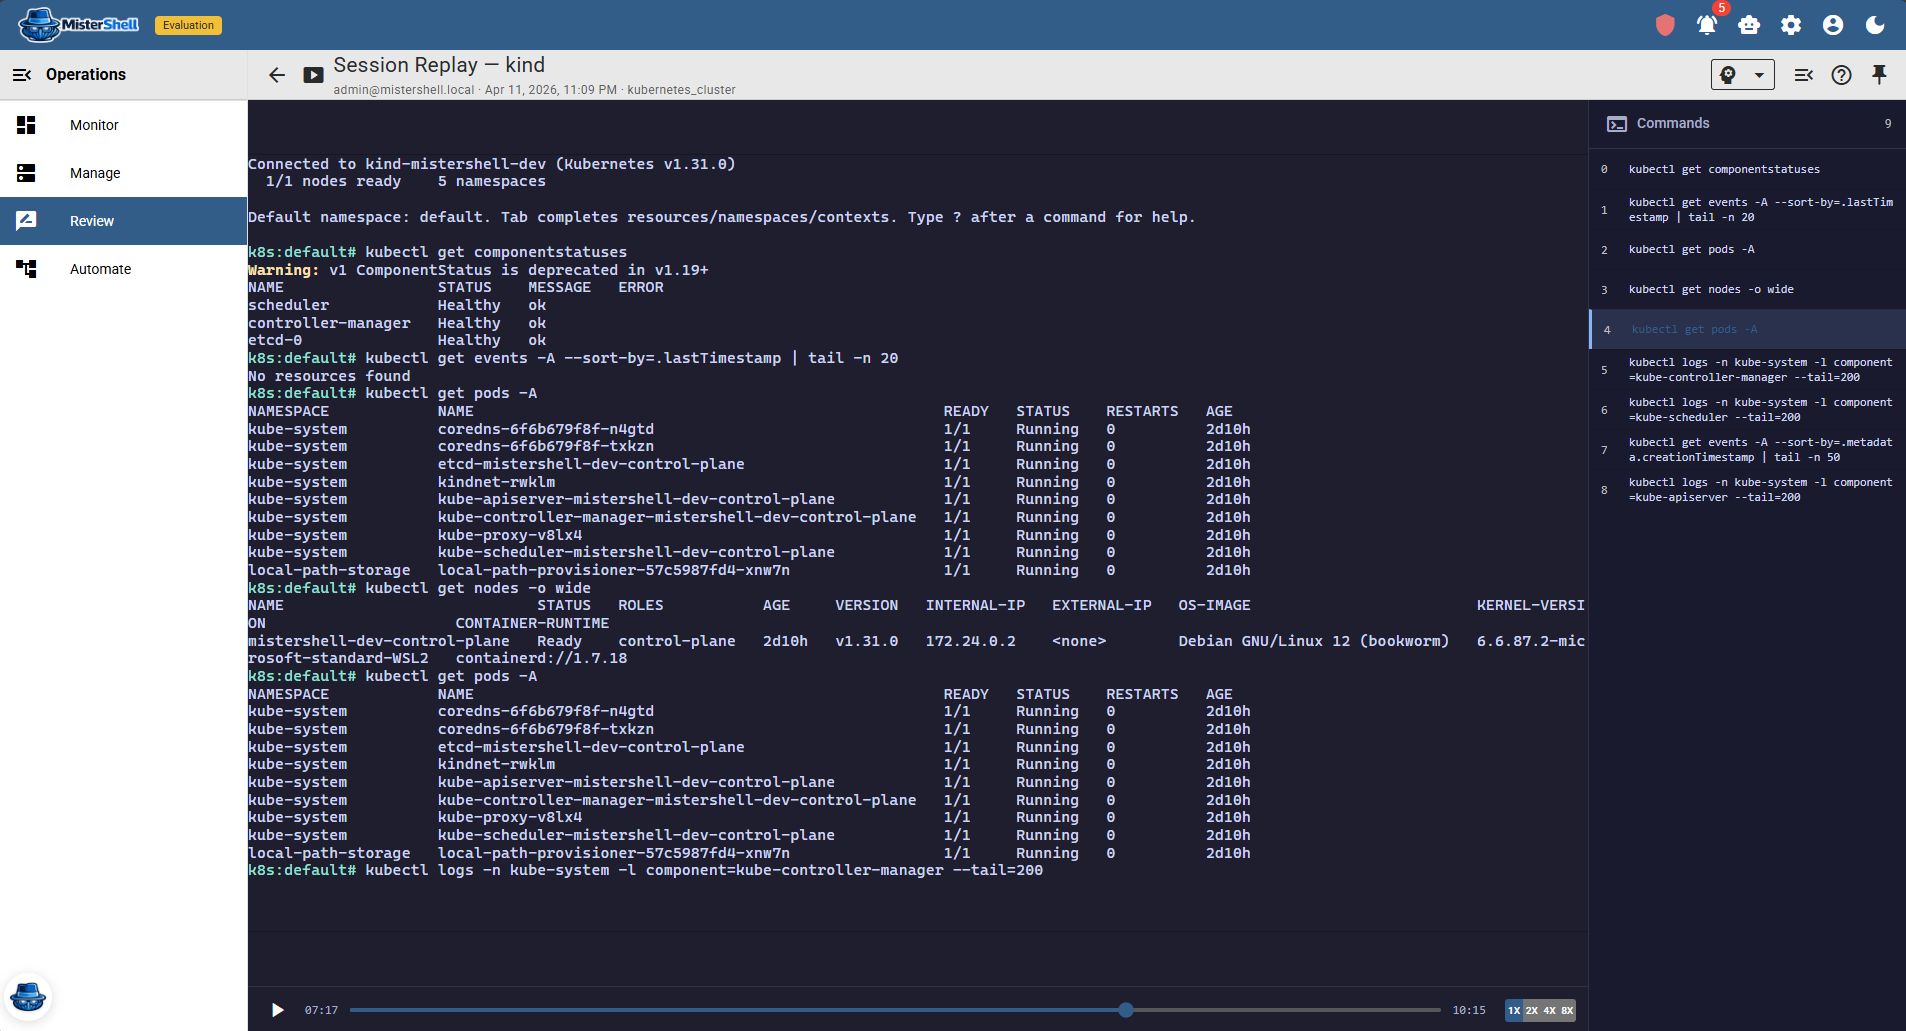
Session recording and replay, governed by policy
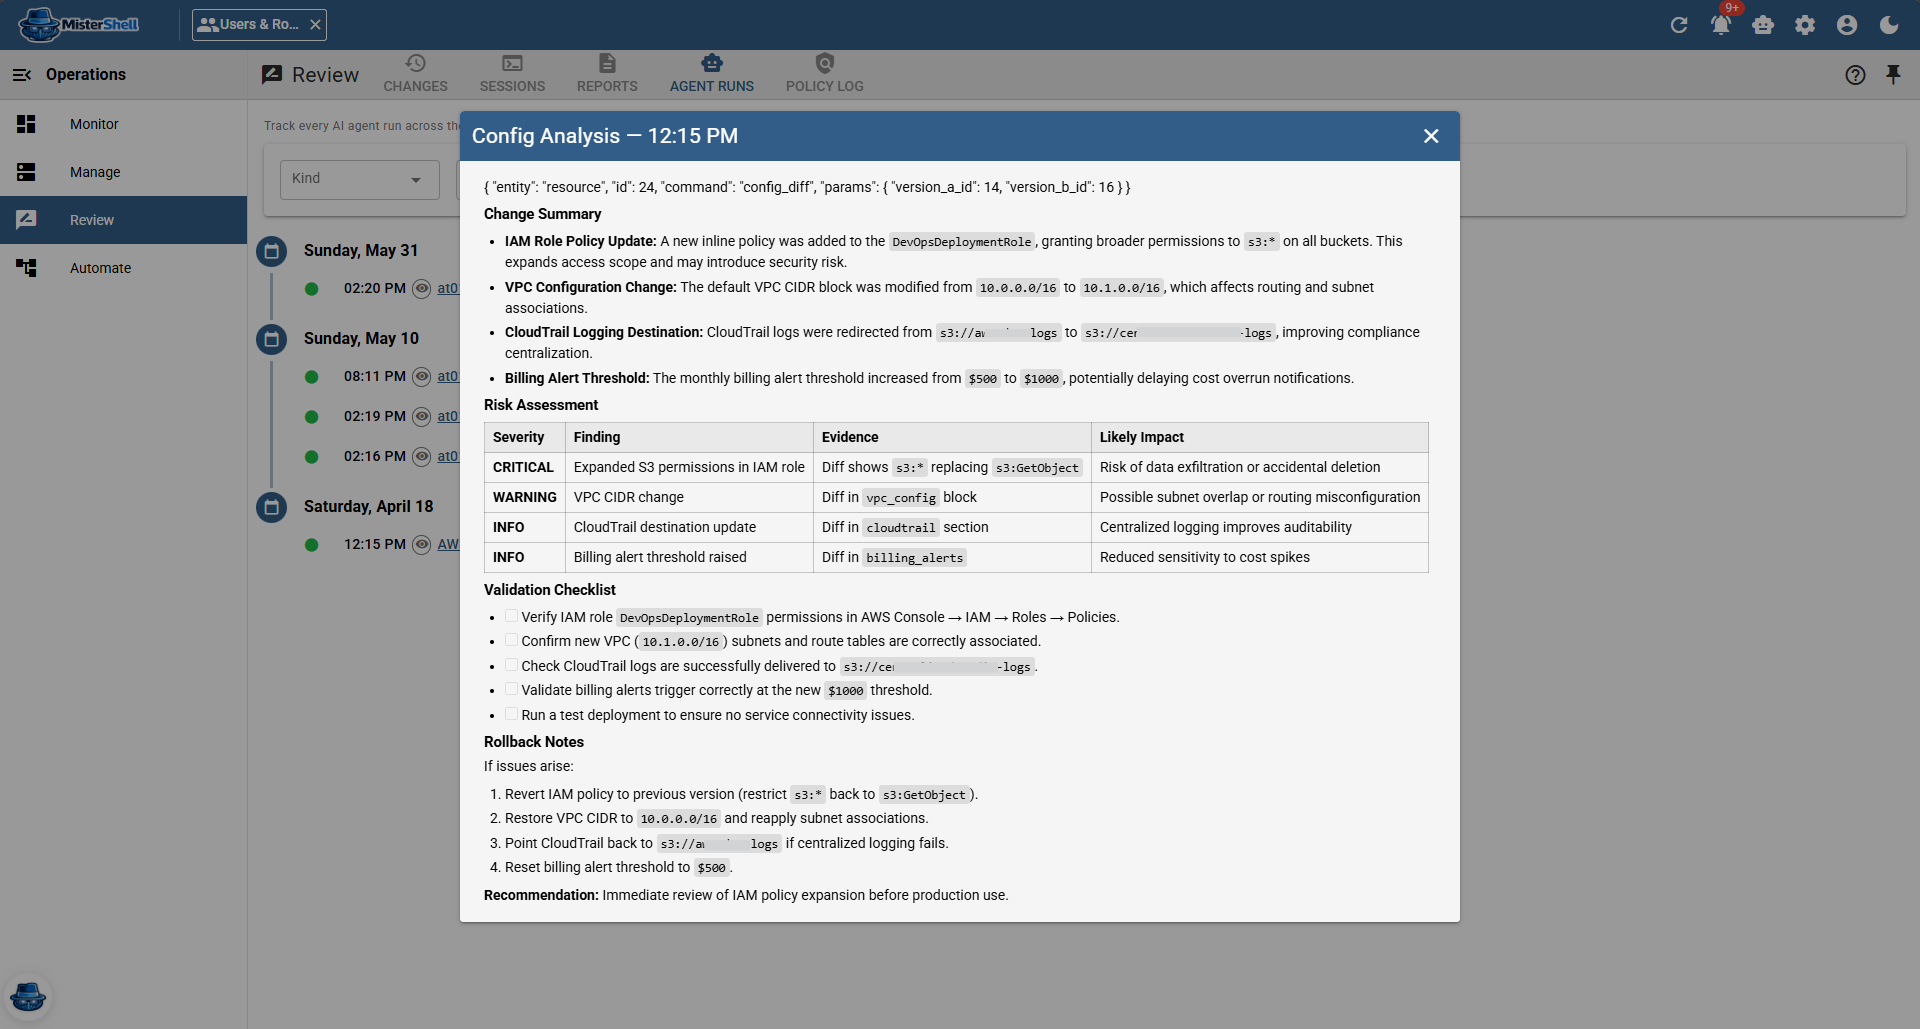
AI agent runs — config analysis with risk assessment, tracked and audited
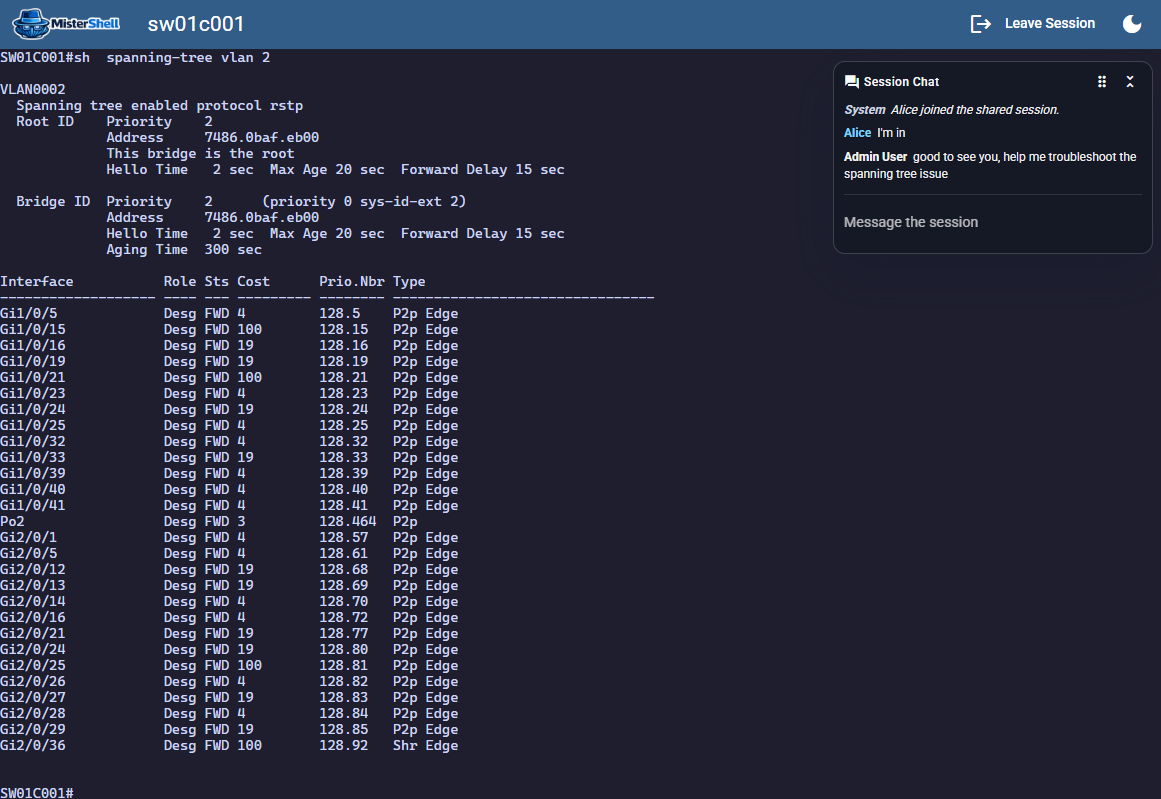
What an invited external guest sees — one shared session, minimal UI, and in-session chat
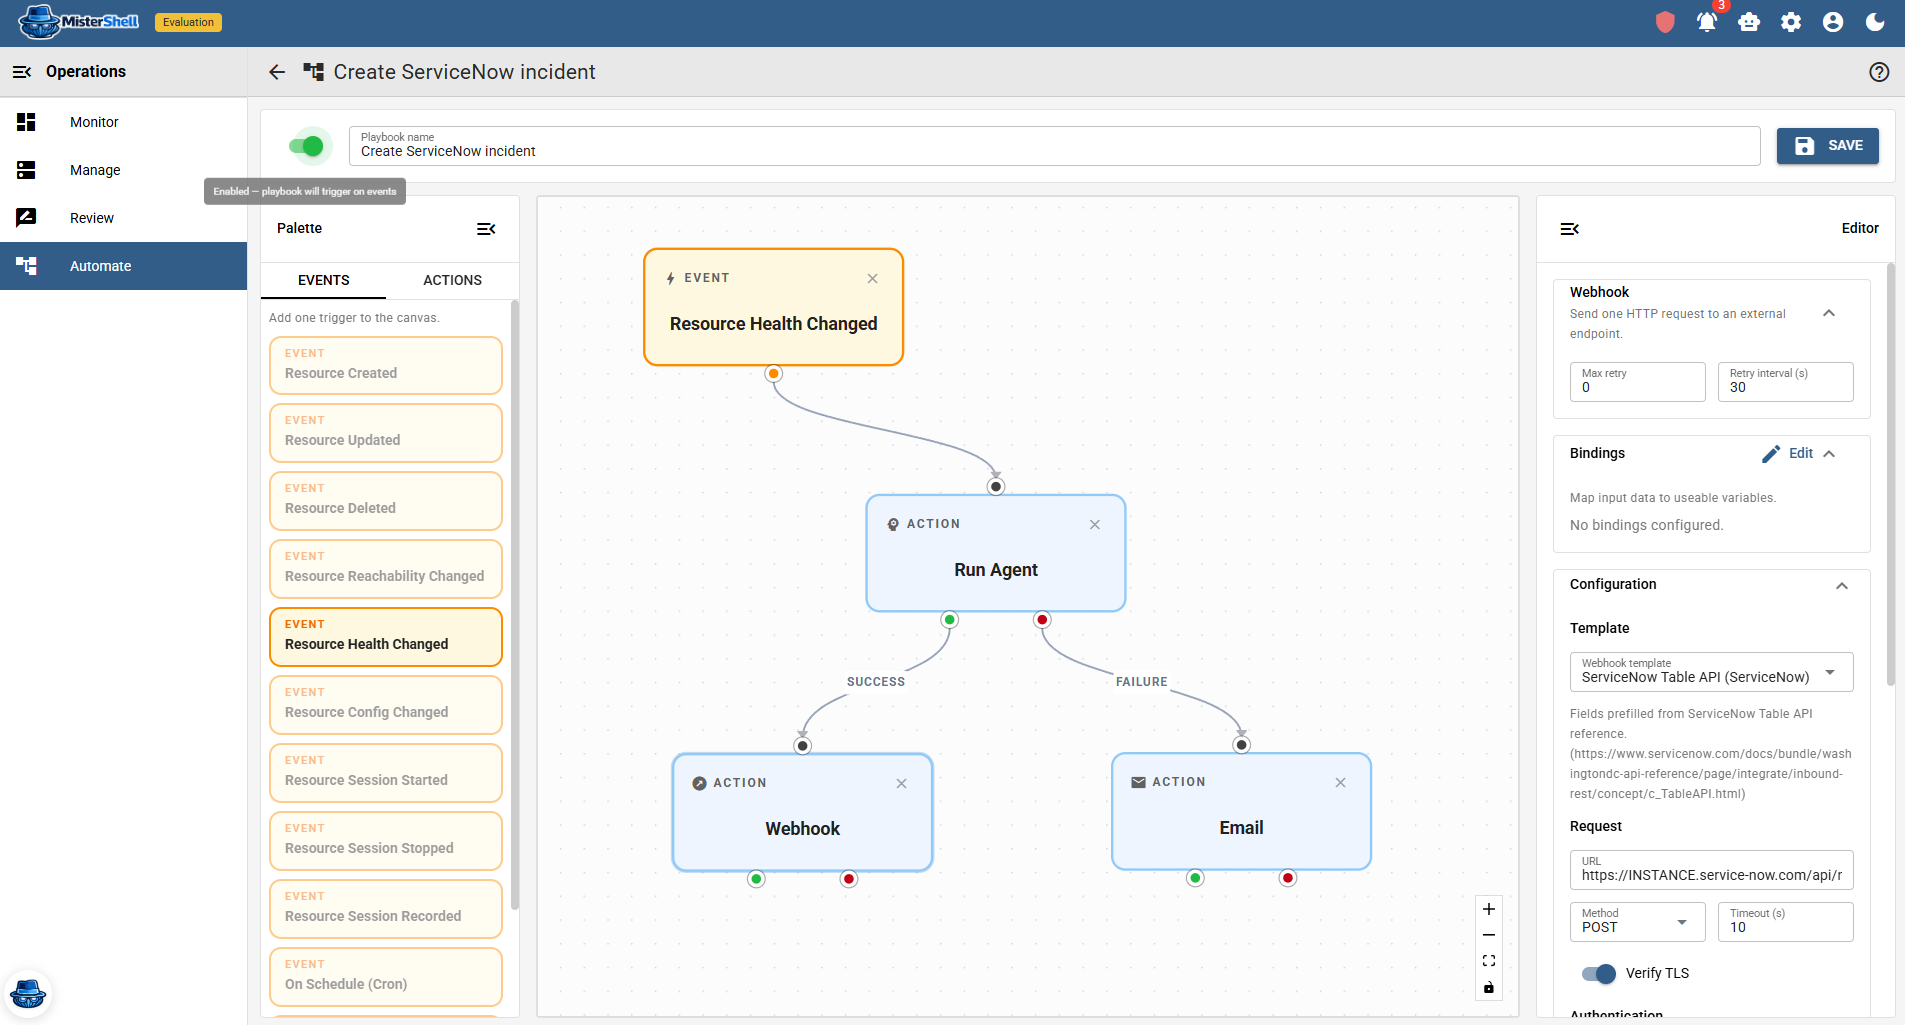
Visual playbook editor for automated workflows
Who runs on it
One platform, every team that runs infrastructure
Pick where your work is — systems, network, platform, or security. Each gets its own depth, on the same fabric, with one policy and one audit trail underneath.
Systems & endpoints
- Reach every Linux and Windows box from the browser or your own SSH client — SSH and RDP, one workflow
- See config and change history without logging in
- Troubleshoot live with an AI assistant that already knows the box
- Every session attributed, recordable and replayable by policy
Network & OT
- Operate multi-vendor gear without jump-host sprawl — from the browser or the SSH client you already use
- Operational facts — interfaces, MAC, ARP, routes and more — collected without a session, queryable across sites
- Outbound-only workers fit your segmentation; nothing inbound to OT zones
- Invite a vendor to troubleshoot — account-less, over a deployed proxy, recordable by policy
Platform & DevOps
- Browser kubectl and SQL shells — scoped to the resource's own CLI, governable per command
- Inventory, roles and session policy as code — the Terraform provider puts access rules in a pull request
- Keep your Ansible playbooks — they reach devices through MisterShell, under the same policy
- Reach it from your AI agent over one governed MCP endpoint
- Automate actions on live events — config change, health, alert
Security & SOC
- One policy model, command ACLs and access approvals across every resource and team
- Session recording and replay — terminal and graphical alike — for any investigation
- Forward audit events straight to your SIEM
- AI works under its own guardrails — read-only by default, every action attributed
Get in Touch
Want a guided demo, or a trial license to evaluate Pro or Enterprise on your own infrastructure? Tell us — we'd love to hear from you.